Get Back to Business with Okta Resilience
Identity is the first thing attackers target and the last thing you can afford to lose. Rubrik Okta Resilience gives you a clear path back: a protected Okta tenant, deep visibility, precise undo, and recovery that keeps Okta and Active Directory (AD) in lockstep.


Vulnerability to Tampering
Backups, stored on-platform with no airgap, are vulnerable. Okta offers limited retention and can’t easily reverse unwanted changes. This complicates forensics, hurts compliance, and extends recovery.

Blind Restores & Silent Failures
Okta is a complex web of interconnected objects with no native dependency mapping. Restoring objects in the wrong order means operational failure and broken access, keeping the business offline.

The AD Dependency Threat
Restoring Okta against a compromised or out-of-sync AD can bring the attacker back and break provisioning automation.
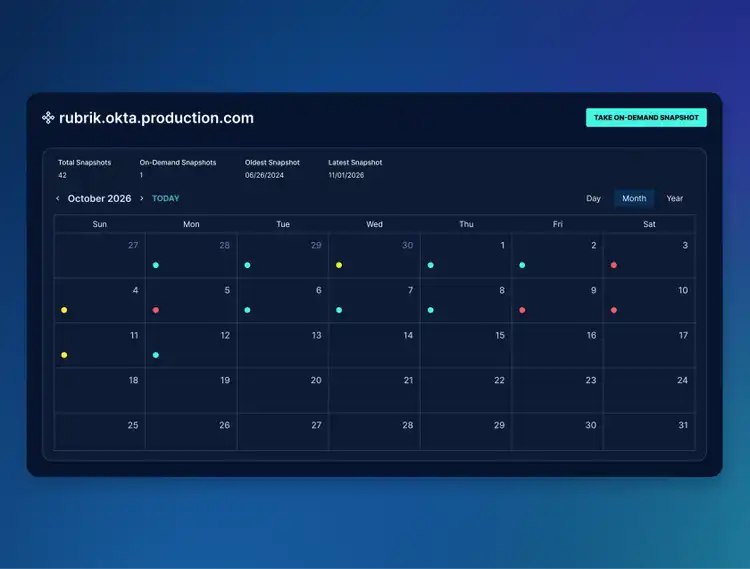
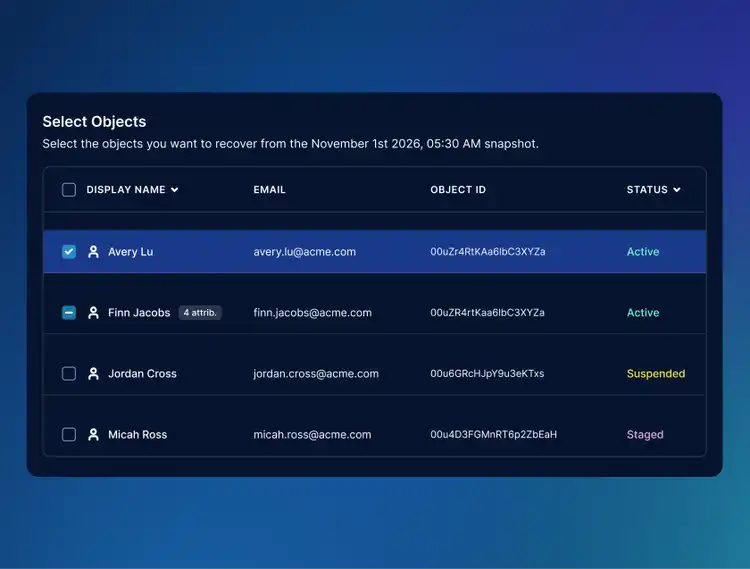
Integrate and validate your tenant through the Okta Integration Network (OIN) with OAuth2 and no backup infrastructure to deploy or manage.
- Our OIN-verified application facilitates a rapid, user-friendly setup
- Immutable, airgapped backups sit in a Rubrik-managed vault outside your tenant, so a compromised admin cannot delete or alter them
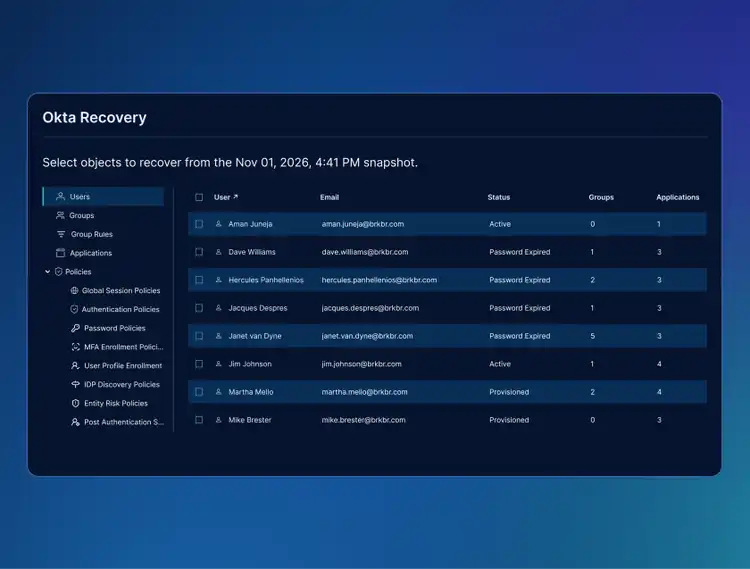
- Protect users, groups, group rules, applications, authentication, MFA policies, and authorization servers with SLA-driven or on-demand snapshots
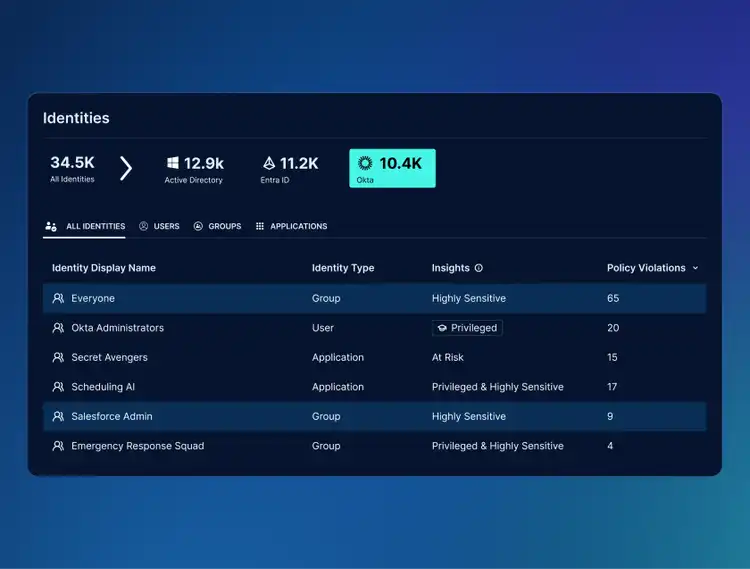
Get deep visibility of Okta users, groups, and relationships. Protect critical objects, configurations, and workflows so that you don’t have to rebuild by hand.
- Protect lifecycle management configurations: provisioning settings, push groups, profile mappings, group rules, event and inline hooks
- Keep identity automation running. Protect Okta SSO (Single Sign-On), LCM (Lifecycle Management), and JML (Joiner-Mover-Leaver) workflows
- Recover Okta identities and configurations into a new clean tenant, simplifying incident response or safely testing changes
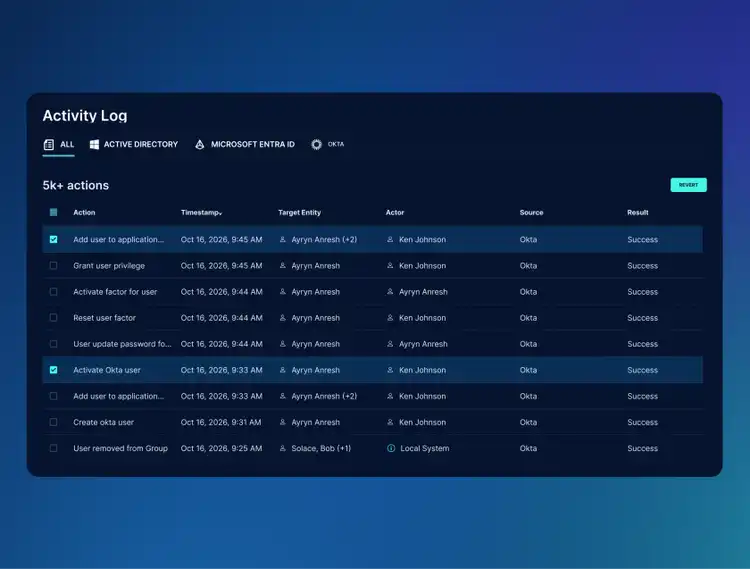
Record changes as they happen. Okta audit and sign-in logs flow into an immutable activity log, where you can watch high-impact events such as admin role grants, MFA policy edits, questionable permission grants, and group membership shifts.
- Get a tamper-resistant record of who changed what and who signed in from where
- One-click revert of unwanted changes directly from the activity log
- Intelligent API throttling adapts to Okta rate limits during bulk backup and restore
Identities flow from Active Directory into Okta, and Rubrik allows you to recover them together. If the full tenant is compromised, restore identities, groups, and admin roles into a separate tenant altogether.
- Recover Okta with the foundation of a verified clean AD, so identity data stays in sync
- Quickly stand up a minimum viable tenant and recover identities, group memberships, and other objects during a full compromise
- Surgically revert select changes or recover your whole tenant
Continuity Across Hybrid Environments
Prevent a failure or misconfiguration from disrupting your entire business. Rubrik helps ensure uninterrupted operations across Okta and AD, so identities, access, and applications stay online.
Dependency-Aware Okta Recovery
Reduce the risks of broken links and manual troubleshooting. Rubrik’s unified recovery workflows automatically account for the complex interdependencies between identity systems, orchestrating restoration in the correct order every time.
Effortless Control from a Unified Console
Simplify management and accelerate incident response. Protect your critical identities, from Okta configurations and workflows to AD and Entra ID objects, in a single, intuitive console designed for complex environments.



SAFE HARBOR: Any unreleased services or features referenced on this page are not currently available and may not be made generally available on time or at all, as may be determined in our sole discretion. Any such referenced services or features do not represent promises to deliver, commitments, or obligations of Rubrik, Inc. and may not be incorporated into any contract. Customers should make their purchase decisions based upon services and features that are currently generally available.