split
true
white-70
IDENTITY RESILIENCE FOR ACTIVE DIRECTORY AND ENTRA ID

Protect & Recover Active Directory and Entra ID

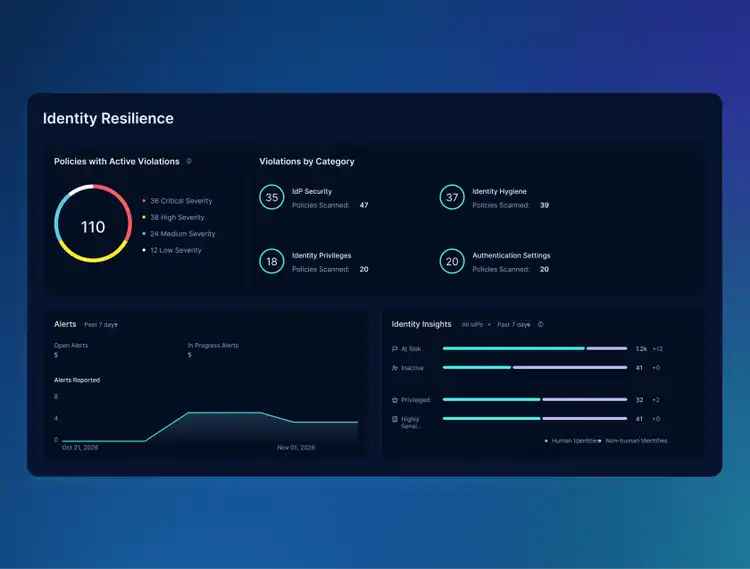
When attackers own identity, access to resources breaks and business stalls. With Rubrik Identity Resilience, restore Active Directory (AD) and Entra ID to a verified clean and current state. Remove attacker persistence and roll forward legitimate changes to get multi-IdP systems back in hours, not weeks.
Get a Demo
button
primary
lg
true
full
Talk to Us
button
secondary
lg
true
full
link
primary
lg
true
full
false
tickerSpeed
20
FEATURED
What's New with Rubrik Identity Resilience
Analyst Report
Get Gartner’s 2026 Backup and Recovery Playbook
Read report
BLOG
Learn how Identity-First Recovery (IFR) Restores AD, Clean and Fast
Discover how Rubrik’s IFR decouples the OS from identity data to restore a clean directory up to 56% faster.
Read blog
_self
BLOG
Read about Rubrik’s Enhanced Entra ID Protection
Rubrik has extended Entra ID protection across governance policies, Intune configurations, and cross-tenant recovery.
Read blog
_self
variant
center
heading
AD and Entra ID are the Foundation of Enterprise Access. Are they Secure?
subheading
Attackers don’t break in anymore. They log in. Once they hold a privileged account in Active Directory or Entra ID, they can create backdoors, change policies, and plant persistence that survives a standard restore.
backgroundColor
bg-white
stat
9 in 10
Intrusions involve Active Directory1
Source: DarkReading
stat
100+
pages involving 29 manual steps for ADFR2
Source: Microsoft
stat
30 days
Entra ID recycle bin limit, with no support for hard-deleted objects3
Source: Microsoft
40
40
Protect & Recover AD and Entra ID before an Identity Incident becomes a Business Outage
Restore your hybrid identity estate. Recover clean and current. All in a single console.
Identity Resilience
Scan for Threats. Surface Risk. Recover Fast.
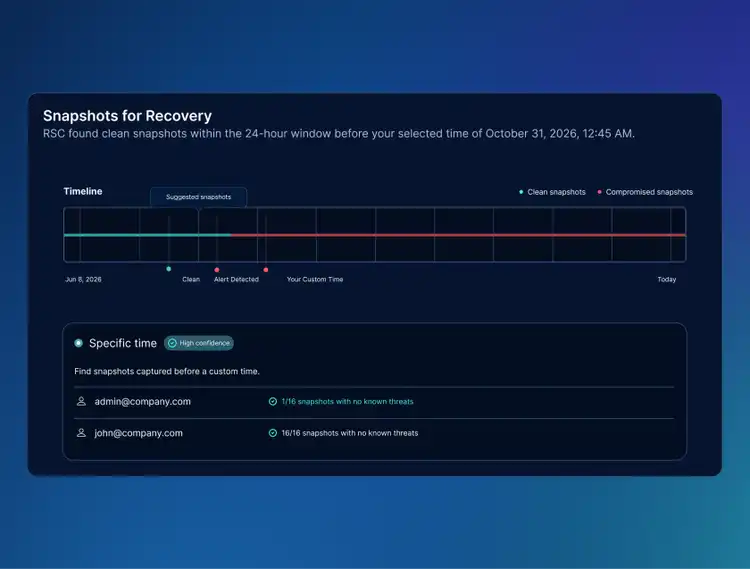
Proactively scan AD backups for threats, surface unsafe configurations, and identify a clean point to recover. Start quickly with out-of-the-box policies and alerts or configure your own. Automatically discover domains, domain controllers, FSMO roles, DNS, and DHCP. Build ready-to-go recovery plans that you can trigger during an incident.
false
false
link
primary
md
true
content
IFR
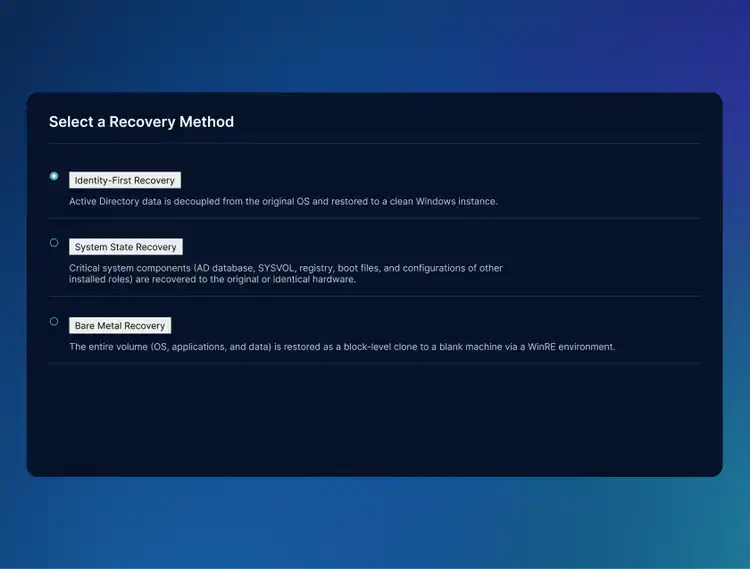
Identity-First Recovery (IFR) for AD
Proactively check AD snapshots for known IoCs and confidently select a known-good point in time. Scan the target OS for risk and make sure it’s clean. Introduce the extracted ntds.dit, SYSVOL, and AD-integrated DNS into a clean Windows instance, enabling portability across on-prem, hypervisors, and cloud. Cut RTO up to 56%.
false
false
link
primary
md
true
content
Roll Forward
Erase Persistence, Not Progress
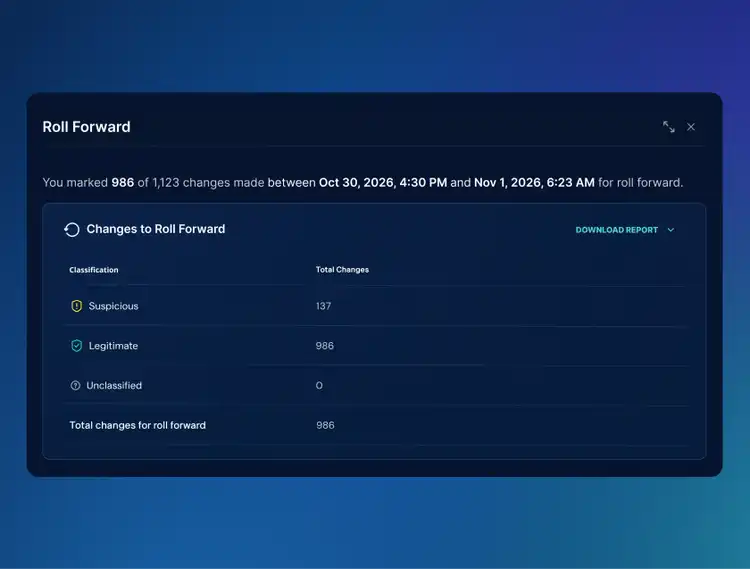
Recover to a clean and current state for AD and Entra ID. Remove attacker footholds. Rubrik’s Identity Intelligence Fabric aggregates context from authoritative systems like ITDR (CrowdStrike/Microsoft Defender), IGA (Sailpoint), and HRIS (Workday) to avoid manually cross-referencing spreadsheets. Review unexplained activities and roll forward only legitimate changes. Keep months of business progress.
false
false
Get a demo
link
primary
md
true
content
Dependency-Aware Identity Recovery
Recovery that keeps relationships intact
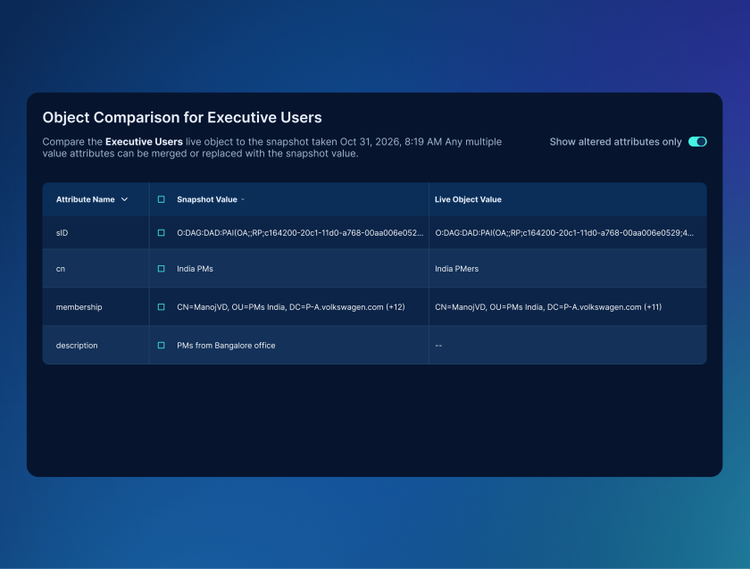
A restored object that gets a net-new SID or GUID breaks the groups, applications, and sync links pointing to the original. Rubrik solves this by restoring objects with all attributes and dependencies intact. Better yet, you can compare entire objects or individual attributes against both snapshots and live data, allowing you to execute granular recoveries and isolate only the specific attributes that need to be reverted.
false
false
link
primary
md
true
content
40
40
M365
Could you recover Microsoft 365 after an identity compromise?
Attackers take over Microsoft 365 by compromising identity. Restore data without removing them from Active Directory and Entra ID, and they walk back in. Recover identity clean separately from the data, and the access can break, further slowing recovery. With Identity Resilience you can:
Recover identity and data together. Restore Entra ID, Active Directory, and Microsoft 365 from one platform, in the right order, with user access restored so people can get back to work.
Remove the attacker, keep the progress. Strip attacker persistence from Entra ID without losing legitimate changes made since the breach.
Protect more of Entra ID. Go beyond users, groups, and roles to cover Conditional Access Policies, App Registrations, Governance Policies, and Intune Settings.
40
40
40
40
Resilience for your Hybrid AD and Entra ID Identity Estate
Fragmented tooling and disconnected workflows slow incident response and increase risk. With RSC, you can protect AD and Entra ID for consistent defense and dependency-aware recovery no matter the threat.
ADFR: Recover in Hours, not Weeks

An attacker compromises an AD domain controller and starts encrypting connected systems. Native ADFR guidance runs 100+ pages and 20+ manual steps. One missed step means starting over while the business stays down. Rubrik fixes this:

  • Automatically scan backups for IoCs. Detect malicious changes via integrations with third parties and monitor activity in the IdP
  • Orchestrate ADFR to a clean state with a 5-click AD recovery wizard
  • Recover individual DCs back to the same host. Conduct ADFR and recover to new Windows hosts, cloud VMs, or bare metal infrastructure.|
  • Roll Forward legitimate changes that happened since compromise

Learn More →

Entra ID: Granular or Full-Tenant Restore

An attacker compromises an admin account and silently alters conditional access policies. Entra's 30-day Recycle Bin is limited; it doesn’t catch hard deleted objects (including objects that don't support soft delete) and doesn't capture policy changes. Discovering broken object dependencies during crunch time means delayed recovery. With Rubrik, you can:

  • Run granular, dependency-aware object recovery so that identity data comes online correctly the first time and access doesn’t break
  • Recover cross-tenant to a standby Entra ID tenant
  • Recover Intune policies, LAPS passwords, BitLocker recovery keys, machine metadata, and governance configs alongside Entra ID. Avoid a disruptive full-tenant restore.
  • Restitch Entra ID and M365 data so that identity and access to resources come online together
Learn More→

true

86%

FASTER RTO

Renown Health cut cyber recovery time from 24 hours to 3 hours after moving identity recovery onto Rubrik. No manual, error-prone ADFR required.
- Renown Health

Healthcare Company

https://www.rubrik.com/customers/renownhealth

3

HOURS

Integris Health cut AD recovery time from 11 days to 3 hours. By going from manual processes to automated recovery, they could restore AD in hours and focus on what matters most: patients.

INTEGRIS Health

Healthcare Company

https://www.rubrik.com/customers/integrishealth

170

Million Health Records

“Without the ability to go back to a verified clean point in time and roll forward without the attacker's changes, you cannot confirm it is actually over. That uncertainty is what immutable backup and point-in-time recovery solves.”

- Kevin Watkins

Director of Cybersecurity, Telus Health

https://www.rubrik.com/customers/how-telus-health-built-cyber-resilience-across-global-health-platform-rubrik

RESOURCES & EXPERTISE

Learn more from our experts

WHITE PAPER
17 pages
How It Works: Protect Microsoft Entra ID
Learn about the features, architecture, and workflows you need to protect Microsoft Entra ID with Rubrik Security Cloud.
Download white paper
Data Sheet
2 PAGES
Restore AD and Entra ID to a Trusted State
Learn how Rubrik helps you protect and recover Active Directory, Entra ID, and hybrid environments.
Download data sheet
WHITE PAPER
8 min read
Identity Resilience: A Technical and Strategic Framework for Service Providers
Rubrik offers service providers a Zero Trust platform to maintain operational continuity and simplify compliance through immutable identity backups, continuous risk monitoring, and automated recovery for hybrid environments.
Learn more
_self
1334595508
FAQ
Everything you need to know
bg-surface-muted
How does Rubrik Identity Resilience improve Active Directory Forest Recovery (ADFR)?
Traditional ADFR relies on over 100 pages of Microsoft guidance and 29+ manual steps, where one mistake can force you to start over. Rubrik automates ADFR with a five-click AD recovery wizard. With Rubrik, you can cut recovery times from weeks or days down to just hours.
Can I recover to a clean state without losing legitimate changes made since the attack?
Yes. Roll Forward recovers AD and Entra ID to a clean and current state. Rubrik’s Identity Intelligence Fabric pulls context from ITDR (CrowdStrike, Microsoft Defender), IGA (SailPoint), and HRIS (Workday). Remove attacker footholds and roll forward only legitimate changes, keeping months of business progress.
How does Rubrik protect Entra ID beyond the native 30-day Recycle Bin?
The Entra ID Recycle Bin is limited to 30 days. It doesn’t support hard-deleted objects and doesn’t capture policy changes. Rubrik covers users, groups, and roles, plus Conditional Access Policies, App Registrations, Governance Policies, and Intune settings. You can run dependency-aware, granular recovery or recover cross-tenant to a standby Entra ID tenant.

white

70%

Learn how Rubrik makes it easy to protect AD and Entra ID. No sales call needed.

Protect & Recover AD

button

primary

md

true

full

Protect & Recover Entra ID

button

secondary

md

true

full

SAFE HARBOR: Any unreleased services or features referenced on this page are not currently available and may not be made generally available on time or at all, as may be determined in our sole discretion. Any such referenced services or features do not represent promises to deliver, commitments, or obligations of Rubrik, Inc. and may not be incorporated into any contract. Customers should make their purchase decisions based upon services and features that are currently generally available.