split
Big Earth
true
white-70
IDENTITY RESILEINCE

Every Cyber Recovery Starts with Identity Resilience

Rubrik Identity Resilience removes attacker persistence and recovers Active Directory (AD) and Entra ID to clean and current on a unified platform. Cut identity attack recovery time by up to 99% without losing weeks of business progress.
Get a Demo
button
primary
lg
true
full
Talk to Us
button
secondary
lg
true
full
link
primary
lg
true
full
1234956249
false
tickerSpeed
20
Renown logo
Americas Test Kitchen logo
Colchester Institute logo
Dunn Lumber logo
Langs Buildings logo
Integris health logo
Nolato logo
Request a demo
button
primary
lg
true
_self
full
icid?2222
Overview
Capabilities
How it works
Resources
FAQ
Get Started
FEATURED
What's New with Rubrik Identity Resilience
Analyst icon
Analyst Report
Get Gartner’s 2026 IAM Backup and Recovery Playbook
Read report
Assessment icon
ASSESSMENT
Take Rubrik's Identity Attack Readiness Assessment
Get a custom risk report
_self
Developer icon
DATA SHEET
Learn how to Recover to Clean and Current
Download datasheet

Identity is your new single point of failure. AI-accelerated attacks ensure you’ll be breached. Rubrik Identity Resilience prepares you for what comes next.
40
40
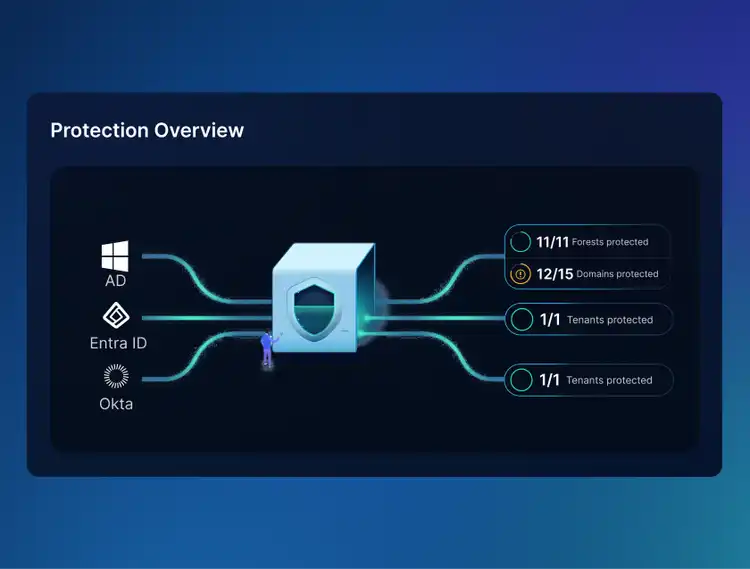
Identity Resilience for AD, Entra ID, and Okta
Identity Resilience for the AI Era
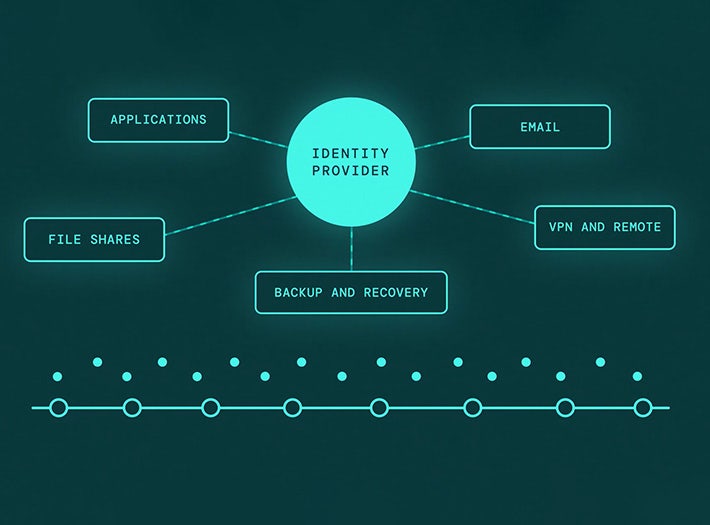
Rubrik Identity Resilience is the industry's only unified platform that returns you to a clean and current state. With Rubrik, you can recover identities on multiple IdPs, remove persistence mechanisms, and safely roll forward legitimate changes.
Return to Clean and Current

Restore to a trusted clean point and safely roll forward legitimate changes since. Use context signals from Rubrik’s Identity Intelligence Fabric that includes ITDR, IGA, and HRIS signals to reconcile actions.

Remove Attacker Persistence

Your incident isn’t closed while their backdoor is still open. Return your identity estate to attacker-free and business-current.

Unify Resilience Across IdPs

One platform to recover identities across your IdPs, whether on-prem or in the cloud. Recover in hours, not weeks.
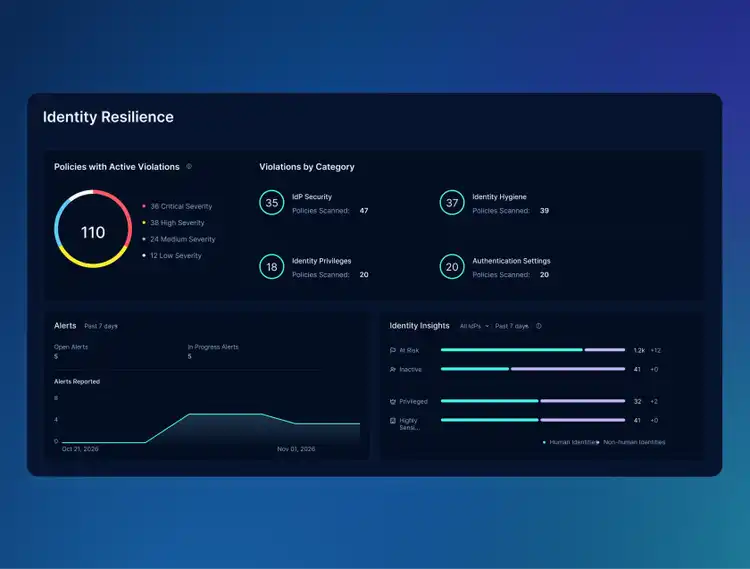
One Platform. Full Identity Resilience.
From proactive monitoring to clean and current recovery, covering the full attack lifecycle—before, during, and after a breach.
A Strong Foundation of Tamper-Resistant Backups
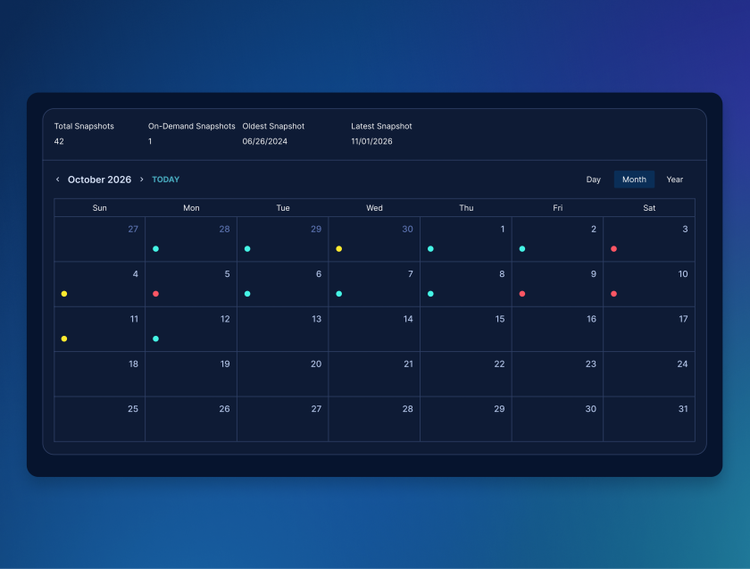
Rubrik Identity Resilience gives you continuous, SLA-driven, physically and logically air-gapped, tamper-resistant backups of identity environments. Have a trusted, clean recovery point untouchable by ransomware or attackers.
Tamper-Resistant Backups
false
false
link
primary
md
false
content
Uncover Vulnerabilities and Have a Plan for Disasters
Proactively scan for threats, surface unsafe configurations, and identify a clean point to recover. Out-of-the-Box or user-defined alerts and policies alert you to unwanted changes. Build ready-to-go recovery plans that trigger during an incident. In a crisis, don't manually sift through backups or choose between compromised systems and massive data loss.
Uncover Vulnerabilities
false
false
link
primary
md
false
content
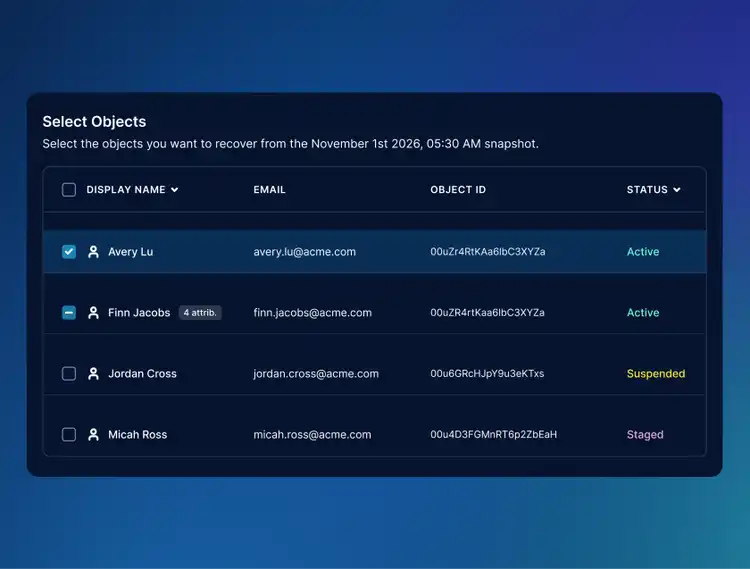
Erase Persistence, Not Progress
Recover to a clean and current state. Remove attacker footholds. Rubrik’s Identity Intelligence Fabric aggregates siloed identity signals so that you can automatically reconcile IdP changes against your ITDR (CrowdStrike/Microsoft Defender), IGA (Sailpoint), and HRIS (Workday) tools. Review only unexplained activities and roll forward legitimate updates. Keep months of business changes.
Erase Persistence
false
false
Get a demo
link
primary
md
false
_self
content
Multiple IdPs. One Platform.
Consolidate your identity estate (AD, Entra ID, and Okta) into a single console, removing the blind spots and tool sprawl of legacy identity security tools and siloed SaaS point solutions. On-prem and cloud are in one platform. Your identity estate is protected—no more silos, blind spots, or unmitigated risk.
Multiple IdPs
false
false
link
primary
md
false
content
Expanded Okta Protection with AD Recovery
Recover Okta backed by a fully synced AD. Back up Okta LCM automation configurations (provisioning settings, mappings, rules, and hooks) and JML workflows. Restore users, groups, apps, and assignments with dependency-aware intelligence to prevent broken links and manual rebuilds. Recover identities and configurations into a clean new tenant for simpler incident response or safe change testing. Recover from one platform to reduce TCO and tool sprawl.
Expanded Okta
false
false
link
primary
md
false
content
How Identity Resilience Works
One identity resilience platform to secure, monitor, and recover identities.
Before an Attack
Find the gaps before the attacker does.

Continuous posture monitoring across AD, Entra ID, and Okta surfaces dormant accounts, privilege escalations, and risky configurations before attackers exploit them. Scan backups continuously against threat intelligence so a clean recovery point is on hand. Start quickly with out-of-the-box policies and alerts or configure your own.

  • Physically isolated backups protected by RBAC, MFA, and TOTP, with unlimited retention. Define and enforce backup frequency, retention, replication, and archival policies.
  • Configure custom policies across IdPs and quantify the blast radius of privileged identities before they’re exploited. Policies are mapped against best practices frameworks like CIS and ISO27001, and regulatory standards like HIPAA, GDPR, and PCI-DSS.
  • Automate AD threat scanning with Threat Hunting and Threat Monitoring. Auto-pinpoint the last known-good state by comparing snapshots.
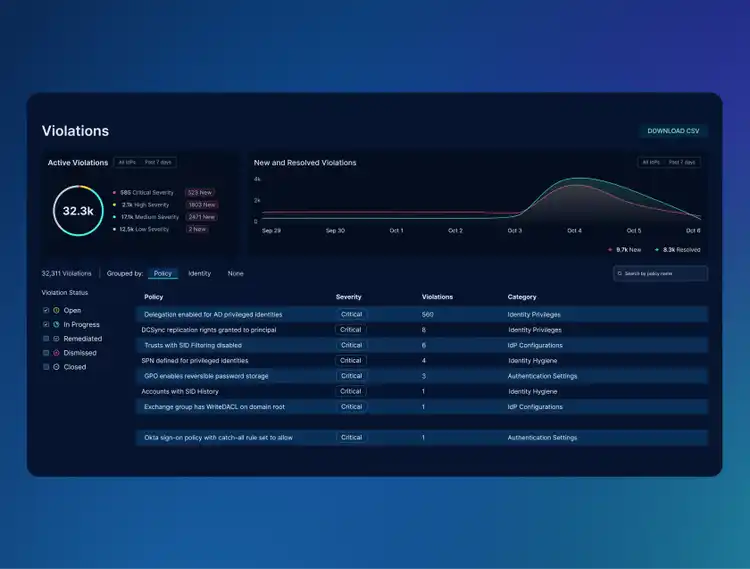
Before an Attack
link
primary
md
true
full
false
false
During an Attack
Know exactly what's happening, as it happens. And stop it.

Every change is tracked in a tamper resistant activity log, and attributed to the actor who made it. This stays intact even if an attacker wipes native logs to cover their tracks. Track which accounts, objects, and permissions are compromised, so you can map the blast radius and start containment. Ensure that nothing an attacker does, or hides, goes unnoticed.

  • Sign-in activity auto-ingests into Rubrik Security Cloud, backed by audit-ready activity and inventory reports.
  • Ingest alerts from integrations with CrowdStrike and Microsoft Defender, automatically correlate alerts with adversary actions, and simplify rollback and recovery to remove persistence mechanisms.
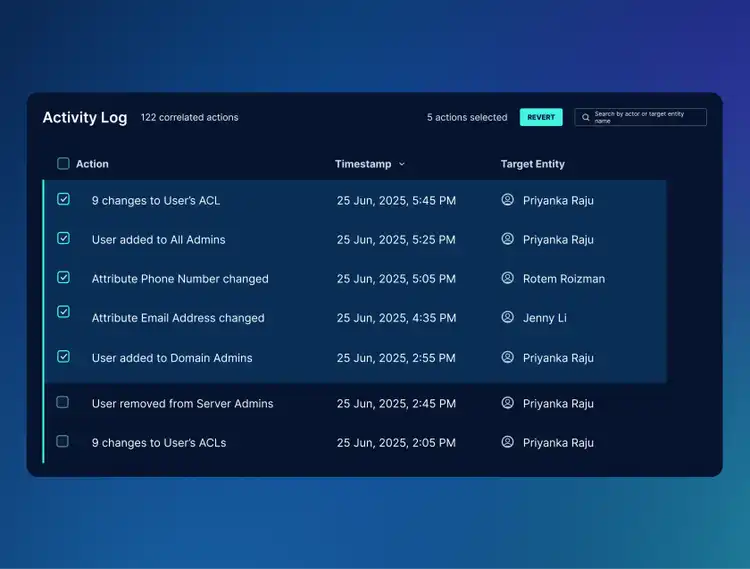
During on Attack
link
primary
md
true
full
tab2
false
false
After an Attack
Recover clean, current, and fast.

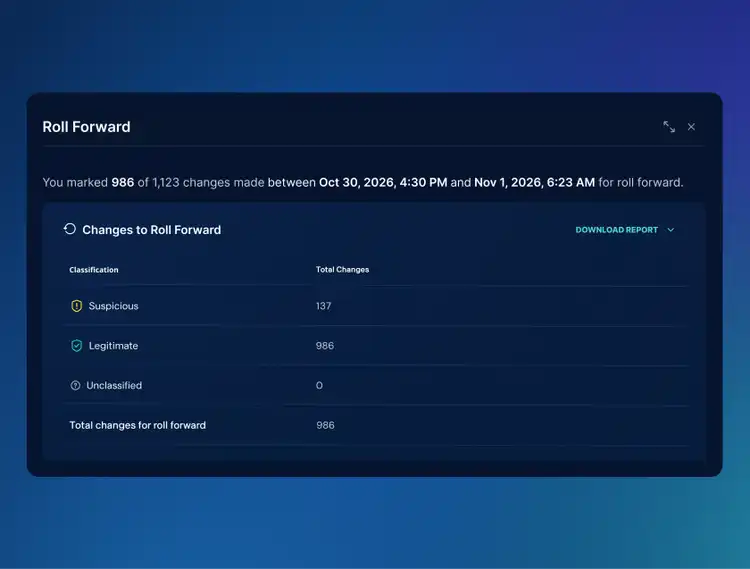
Restore a trusted IdP state in hours, not weeks. Then triage IdP modifications as suspicious, legitimate, or unclassified, and reapply only legitimate changes. That way, clean recovery doesn't cost you months of business progress.

  • Compare the clean vs. current state with context from the Identity Intelligence Fabric. Reconcile what’s true without manually cross-referencing spreadsheets.
  • Evict attackers and keep wanted IdP changes.
  • The directory reflects the business today, not a stale snapshot.
  • Detailed logs with actor attribution and timestamps simplify audit, compliance, and reporting across IdPs.
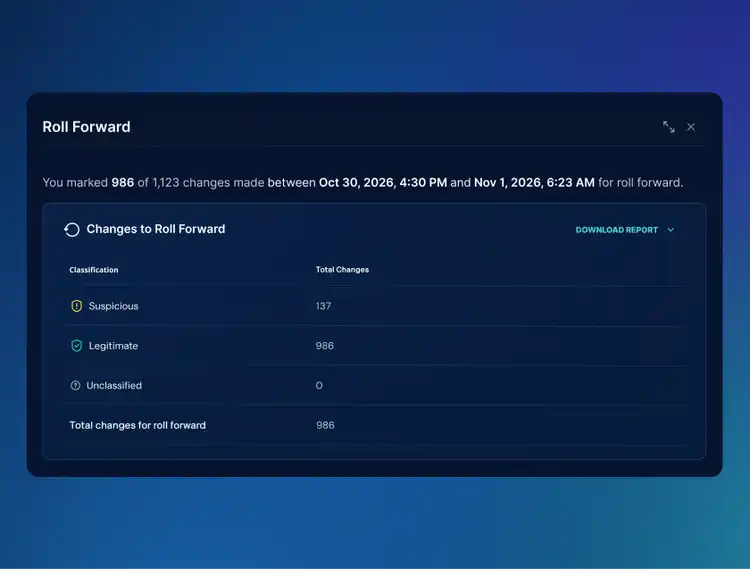
After An Attack
link
primary
md
true
full
false
false
true
Renown health

86%

FASTER RTO

Renown Health cut cyber recovery time from 24 hours to 3 hours after moving identity recovery onto Rubrik. No manual, error-prone ADFR required.
Renown health logo

- Renown Health

Healthcare Company

https://www.rubrik.com/customers/renownhealth

Integris health

3

HOURS

Integris Health cut AD recovery time from 11 days to 3 hours. By going from manual processes to automated recovery, they could restore AD in hours and focus on what matters most: patients.

Integris logo

INTEGRIS Health

Healthcare Company

https://www.rubrik.com/customers/integrishealth

Telus health
Telus

170

Million Health Records

“Without the ability to go back to a verified clean point in time and roll forward without the attacker's changes, you cannot confirm it is actually over…[]. That uncertainty is what immutable backup and point-in-time recovery solves.”

Telus logo

- Kevin Watkins

Director of Cybersecurity, Telus Health

https://www.rubrik.com/community/blogs/why-identity-resilience-requires-recovery-floor

RESOURCES & EXPERTISE

Learn more from our experts

whitepaper icon
White paper
17 pages
How it Works: Identity Resilience with Rubrik Security Cloud
Rubrik Identity Resilience is designed to directly address modern identity challenges by providing a comprehensive, unified approach to identity security.
Download whitepaper
How it works
whitepaper icon
DATA SHEET
2 pages
Identity Resilience for Multi-IdP, Hybrid Environments
Secure identity systems with end-to-end protection, visibility, and recovery across your multi-IdP environment.
Download datasheet
img-okta-identity-recovery-16x9.webp
Blog icon
Technical Brief
6 PAGES
Rubrik Identity Resilience
Learn how Rubrik Identity Resilience empowers organizations to protect and recover their identity systems before, during, and after an attack.
Learn more
_self
1334595508
FAQ
Everything you need to know
bg-surface-muted
What is identity resilience?
Identity resilience is the ability to keep identity systems like AD, Entra ID, and Okta operational, trustworthy, and cleanly recoverable through an attack. It goes beyond access management and backup: identity resilience involves detecting malicious IdP changes, seeing who changed what and when if a primary IdP is compromised, and recovering IdPs to a clean state without losing legitimate business progress. Rubrik Identity Resilience delivers all of this on a single platform.
How is identity resilience different from identity and access management (IAM)?
IAM governs who gets access to what; it doesn't help once an identity system is compromised. Identity resilience picks up where IAM stops: detecting malicious changes, containing the blast radius, tracking attacker activity, and recovering a clean, current state afterward. These are the parts of an identity attack that access controls alone can't stop.
What is Active Directory?
Active Directory (AD) is Microsoft’s directory service used to manage, organize, and secure user identities and access permissions across an organization. It acts as the central authority that authenticates and authorizes users to log into devices and connect to internal applications. Beyond basic identity management, AD provides centralized governance through Group Policies, allowing IT teams to enforce security rules and control access across the entire enterprise infrastructure. Rubrik Identity Resilience offers AD security, helping organizations lower ADFR time from weeks to hours.
How fast can Rubrik recover a compromised Active Directory forest?
Native Active Directory Forest Recovery (ADFR) requires following 150+ pages of documentation across 20+ manual steps, where a single mistake means starting over. Rubrik replaces that with a five-click recovery workflow that handles object dependencies automatically, cutting recovery from days or weeks to hours. With Rubrik, Renown Health restored AD to a clean, point-in-time state within hours, not days.
What is Roll Forward, and why does it matter?
Traditional backups force a choice: roll back to a clean snapshot and lose weeks of legitimate changes, or restore to the current state and keep the attacker's persistence mechanisms. Roll Forward removes that trade-off. Rubrik restores identity systems to a clean state, then classifies changes since compromise as safe, suspicious, or harmful, and surgically reapplies only the legitimate updates, preserving months of business progress.
Does Rubrik Identity Resilience replace tools for identity threat detection and response, like CrowdStrike or Microsoft Defender for Identity?
No — it enhances them. Detection tools like CrowdStrike Falcon Next-Gen Identity Security and Microsoft Defender for Identity are built to flag a threat. Rubrik takes it from there: correlating the alert with the actual changes an attacker made and orchestrating the clean recovery, closing the loop from detection to recovery.

white

70%

Watch Rubrik Identity Resilience in action.

Guided Demo

button

primary

md

true

full

button

secondary

md

false

_self

full

SAFE HARBOR: Any unreleased services or features referenced on this page are not currently available and may not be made generally available on time or at all, as may be determined in our sole discretion. Any such referenced services or features do not represent promises to deliver, commitments, or obligations of Rubrik, Inc. and may not be incorporated into any contract. Customers should make their purchase decisions based upon services and features that are currently generally available.