split
BG Earth
true
white-70
CLEAN ROOM RECOVERY

You don’t need to build a clean room. It’s already built-in!

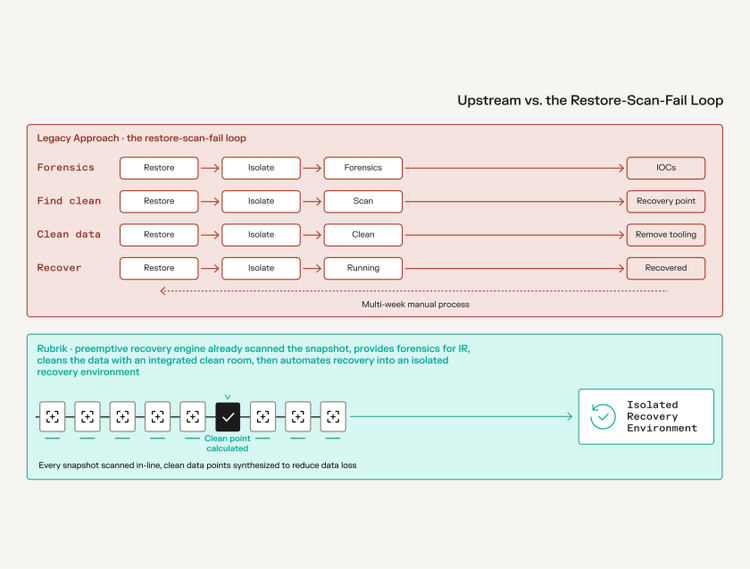
Most clean rooms exist to provide secure access to malware for forensic analysis, find a clean recovery point, clean the data to remove persistence & encrypted data and finally as an isolated recovery environment that you can trust in the event of an attack.

Rather than building these rooms then painfully recovering backups into each one by one; Rubrik has built a fully automated integrated clean room into the platform itself that answers all three clean room use cases, while still giving you multiple options for the final use case of an isolated recovery environment - now it only has to be somewhere clean to recover into.
Watch Demo Now
button
primary
lg
true
_self
full
Contact Sales
button
secondary
lg
true
_self
full
link
primary
lg
true
full
false
tickerSpeed
20
Adobe
carhartt
iron mountain
pepsi
simpson strong tie
the home depot
variant
center
eyebrow
ISOLATED RECOVERY
heading
You still get a clean room, Rubrik changes what you use it for.
subheading

Most rooms are built to compensate for a backup platform that either cannot tell you what is clean, or is needed to clean the data to reduce data loss rather than recovering from multiple days ago.

Rubik's preemptive recovery engine already knows what is clean, has pre-calculated hashes for 0-day attacks, provides secure delivery of malware for forensics, automatically removes malware & encrypted data with an integrated data clean room, then automates recovery into an isolated environment, massively reducing data loss & cyber-RTOs.

backgroundColor
bg-white
stat
BREACHED
74%
Share of organizations reporting attackers reached their backup systems. Which is why what is clean has to be provable, not assumed.
stat
UPSTREAM
60 sec
Time to scan an estimated 75,000 backups, on hashes computed as those backups were created rather than during the incident.
stat
RECOVERABLE
100%
Share of protected data recoverable into the room on one dual-homed cluster, against a typical 20–40% subset when the room needs its own.
40
40
SUPPORTED ARCHITECTURES
Three deployment models. One orchestration layer.
Rubrik determines clean with built-in cyber scanning, so no clean room is required to find clean. Everything below exists for one reason — recovery. The deployment model changes; the orchestration layer does not.
On-premises

Bring your own isolated network zone. One cluster dual-homed across production and the isolated side, or replicate to a dedicated isolated cluster behind an internal firewall, outbound only.

Cloud to cloud

Snapshots replicate across the cloud backbone into a separate dedicated organization, tenant or domain with restricted access. Ephemeral scanners, no on-premises footprint, no ports required.

On-premises to cloud

Workloads recover into a cloud-hosted isolated environment over an encrypted tunnel, on matching hypervisor-as-a-service, or delivered as a fully managed service with runbooks and scheduled tests.

70
50
THE FOUR USE CASES OF AN ISOLATED RECOVERY ENVIRONMENT
Every one of these is a legitimate need. Rubrik removes three of them.
Perform forensics

Rehydrate infected systems into a sandbox so security teams can run the malware, watch it execute, map persistence and extract indicators of compromise.

  • Secure Malware Download pulls the suspect files straight out of the backup without hydration
  • Handed to the IR team in a secure portable password-encrypted archive, for use with their own tools
  • No workload restore, no sandbox to build, no infected VM running
Get the malware, not the machine.
Find a clean recovery point

Restore candidate snapshots into an isolated environment, then boot and scan them one at a time until one comes back clean. Every vendor without in-backup detection needs this room.

  • The Preemptive Recovery Engine determines clean inside the backup itself
  • Every snapshot scanned in-line against auto-updated IOCs with hashes pre-computed
  • Turbo Threat Hunting finds clean in zero-day attacks across hundreds of thousands of backups in seconds
Rubrik already knows which one is clean.
Clean data and staging

Restore into a staging area, manually hunt and strip out the malware, re-scan, revalidate, then promote. Every step sequential, every step by hand.

  • Malware & remote access tooling already quarantined to prevent re-introduction
  • Encrypted data already reverted to its pre-attack version to reduce data loss
  • Integrated data clean room removes malware & tooling for surgical recovery
The data is already quarantined & removed.
Peace-time testing and post-attack recovery

Prove recovery before the incident, and have somewhere clean to recover into when production is compromised, offline, or simply cannot be trusted.

  • Orchestrated isolated recovery across on-premises & cloud with preemptive scanning & clean room to reduce RTO
  • Unique dual-homed appliance architecture for isolated recovery on-premises with 50% less HW
  • Cloud to cloud isolated recovery, multiple options for on-premises to cloud isolated recovery as a service
This is the one you actually build.
variant
center
eyebrow
PART OF THE PLATFORM
heading

The room is the destination. The platform is what makes it worth having.

subheading
Isolated recovery only works if something already knows which copy is clean and has kept it somewhere an attacker cannot reach.
backgroundColor
bg-white
Rubrik Secure Vault

The cyber recovery vault, immutable from the very first backup.

Explore
Threat Analytics

Continuous, in-line scanning of every snapshot as it is created.

Explore
Cyber Recovery

Rapid, predictable recovery to a verified clean state.

Explore
Identity Resilience

Recover Active Directory, Entra ID and Okta without attacker persistence.

Explore
RESOURCES & EXPERTISE
Learn more from our experts
Blog
14 min read
Enhancing your clean room with Rubrik Security Cloud and cyber recovery
How in-backup scanning and clean point selection change what an isolated recovery environment has to do, and what it no longer has to.
Read the blog
Blog
9 min read
Introducing Turbo Threat Hunting: redefining cyber recovery speed
Why pre-computed hashes make scanning an estimated 75,000 backups in 60 seconds possible, and what that replaces.
Read the blog
_self
Report
40 pages
Rubrik Zero Labs: The State of Data Security
Where attackers go once they are inside, how often they reach backup systems, and what that means for how you design recovery.
Read the report
FAQ
Everything you need to know
bg-surface-muted
Do I need to build a clean room if I use Rubrik?
No. Rubrik has a clean room built into the platform, so the three jobs a clean room usually does — forensics, finding a clean recovery point, and stripping malware — all happen inside the platform before anyone provisions anything. What you do still need is an isolated recovery environment: somewhere clean to recover into when production is encrypted, still occupied by an attacker, quarantined, or gone, and proven before the incident rather than during it. Rubrik does not replace that. It changes what it has to do.
How does Rubrik find a clean recovery point without restoring anything?
Every snapshot is scanned in-line as it is created, against auto-updated indicators of compromise, YARA rules and hash matching, so the determination happens inside the backup rather than after a restore. For zero-day attacks, Turbo Threat Hunting works against pre-computed hashes, which is what makes scanning at scale fast enough to matter. In internal testing it scanned an estimated 75,000 backups in 60 seconds. The room was never the detector.
How do incident response teams get malware samples without building a sandbox?
Secure Malware Download pulls the suspect files straight out of the backup and hands them to the IR team in a password-encrypted archive. The team then uses its own intelligence feeds and tooling to build an indicator list. Nothing is restored, no infected workload is ever booted, and there is no sandbox to stand up. Get the malware, not the machine.
What does it cost to add an isolated recovery environment?
Less than the traditional design, and it does not have to be decided up front. The usual approach is a second backup environment inside the isolated zone — two clusters, two licences, two estates to operate. With Rubrik, a single cluster can be dual-homed across production and the isolated side, so the environment becomes a second network interface rather than a second project. You can cable it whenever the business asks. Alternatively, you can deploy a dual-cluster Rubrik solution with an internal firewall for isolation, with the added benefit of a PULL-based replication methodology resulting in RPOs as low as 15 minutes without ever having to open a port in the firewall to update the isolated vault copy, or wait for data to be synchronized to be scanned like legacy solutions.
Where can an isolated recovery environment run?
Three places, all supported. On-premises, in your own isolated network zone. Cloud to cloud, in a separate dedicated organization, tenant or domain with restricted access, fed by replication across the cloud backbone. Or on-premises to cloud, where workloads recover into a cloud-hosted environment over an encrypted tunnel, including as a fully managed service. The deployment model changes; the orchestration layer does not.
How do I prove my cyber RTO before an incident?
By testing recovery in peacetime, non-disruptively, on a schedule. Rubrik orchestrates recovery into the isolated environment with pre-built runbooks that handle boot order, dependencies and failover, so a test is repeatable rather than a one-off exercise. That gives you a measured recovery time rather than an estimated one — which is the number your board, your auditors and your insurers are actually asking for.

white

70%

Walk a clean recovery yourself. Threat hunt, clean point, orchestrated recovery.

Guided Demo

button

primary

md

true

full

Contact Sales

button

secondary

md

true

_self

full